
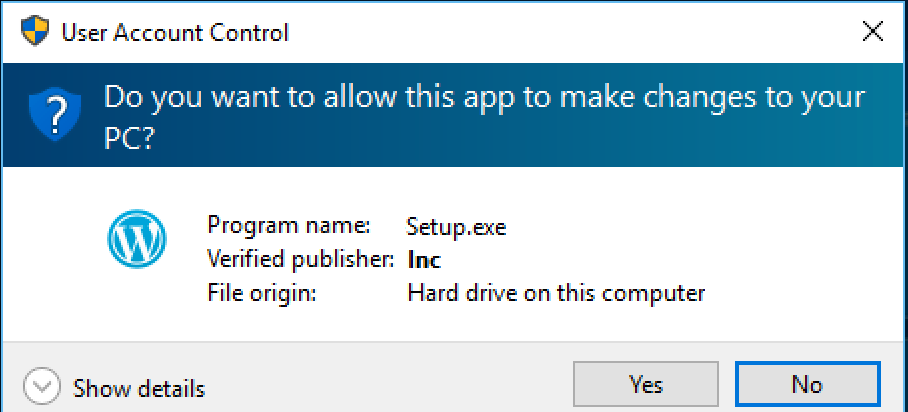
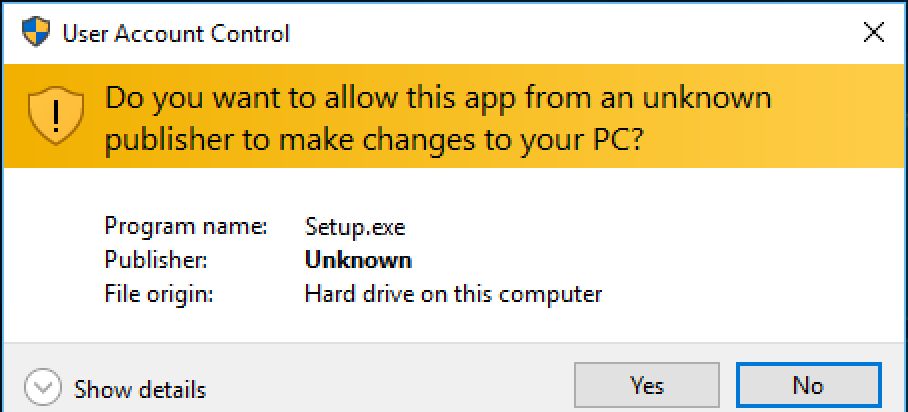
You can publish your application on your website. But Microsoft SmartScreen will not like it at all if the binary is not signed. This is how the same application looks signed and unsigned:
Last reviewed: September 2026 — and this time I bought the certificate myself. Two industry-wide changes reshaped this market since I first wrote this article; if you stop reading now, at least read the next box. The second half of the article is new: what the purchase was actually like, and the bad news nobody puts on the Buy page.
What changed (and why my old advice no longer applies)
The cheap, no-hassle PFX-on-disk workflow I used for years is gone. Two CA/Browser Forum decisions killed it:
- June 2023 — hardware key storage became mandatory for OV too. Until then, EV required a hardware token but OV could ship as a PFX file. Now both require the private key to live on a hardware token (USB), a Hardware Security Module (HSM), or a CA-hosted cloud signing service. You can no longer download a PFX, drop it next to your build script, and call
signtool.exe. If you renew an OV certificate today, this is the rule you fall under. - February 2026 — single-certificate validity capped at 459 days (~15 months). When you buy a “3-year” plan today, you are buying a 3-year subscription, not a single 3-year certificate. The CA issues a new certificate every ~15 months across the term, free. You reissue once per period and re-bind it to your token.
The net effect: most US resellers (SignMyCode, SSL2BUY, sectigostore, ksoftware) only sell their cheap “token + shipping” option on 1-year plans now. To get a 2- or 3-year multi-year discount with them, you must already own an HSM — physical (FIPS 140-2 level 2+) or rented in the cloud (AWS CloudHSM, Azure Key Vault, Google KMS), all of which cost more per year than the certificate itself. So multi-year is now “HSM only” at most US shops.
The way out is cloud signing — a CA-hosted virtual smart card you sign against over the network. No USB stick to lose, no driver to wrestle with, and multi-year discounts are back on the menu.
The cheapest legitimate option in 2026 — Certum cloud OV via SSLmentor
I did the research for you again. The cheapest legitimate path for a small Delphi shop in 2026 is:
Certum Standard Code Signing in the Cloud (OV), 3-year, through SSLmentor reseller — $348 total (= $116/year), no USB token, no HSM.
What you get:
- An OV code signing certificate from Certum (Polish CA, owned by Asseco — same group that runs the Polish national e-ID).
- Cloud-hosted private key. Certum’s free SimplySign Desktop app emulates a smart-card reader on your machine;
signtool.exesees a virtual smart card and signs against it over the network. No physical token to ship, plug in, or lose. - Across the 3-year term, you reissue the certificate inside the Certum panel (a click) every ~15 months. Free.
- EU CA, EU billing — for those of us in the EU, no customs paperwork, no $130 “USB stick shipping fee”.
An independent indie-developer comparison published in early 2026 reached the same conclusion: “No vendor undercuts Certum’s $108/year amortized 3-year rate.”
Price comparison (May 2026)
All prices net of VAT, USD. “True 3-year total” includes mandatory add-ons (token, HSM, or cloud subscription) that the cheap headline price hides.
| Vendor (channel) | 3-year total | Per year | Token / HSM needed? | Notes |
|---|---|---|---|---|
| Certum (via SSLmentor) | $348 | $116 | No — SimplySign cloud | Winner. EU CA. Free reissues across term. |
| Azure Artifact Signing (formerly Trusted Signing) | ~$360 | ~$120 | No — Azure-hosted | Open to the EU since 2026 (also UK, Australia, New Zealand, Japan, South Korea, Singapore, Switzerland, Norway, Israel), and the old 3-years-of-trading rule is gone. The only vendor here that signs unattended — a build server can sign with nobody present. Two catches: the signature verifies only on Windows patched to September 2021 or later (about 1.2% of desktop Windows cannot), and Microsoft will never issue you an EV. |
| SSL.com (cert + eSigner cloud) | ~$867 | ~$289 | No — eSigner cloud | Advertised “$109/yr” is misleading: eSigner adds ≥$180/yr on top. |
| SSL.com (cert + own YubiKey) | ~$329 (if you already own a YubiKey 5 FIPS) | ~$110 | Yes — YubiKey 5 FIPS | Vincent Parrett (FinalBuilder) reported on DelphiPraxis: $328.95 for a 3-year OV, using his own YubiKey. A bare YubiKey 5 FIPS costs ~$110–$150 from Yubico; SSL.com’s bundled token is +$379 (they ship it pre-attested). |
| SignMyCode / SSL2BUY (Comodo, Sectigo) | not sold to small shops | $216–$280 | Yes — HSM only for 2/3-year | Token+shipping option is 1-year only since Feb 2026. Multi-year requires “install on existing HSM”. |
| GlobalSign EV (David Heffernan’s choice in the DelphiPraxis thread) | ~$950 | ~$317 | Yes — SafeNet USB shipped | EV, not OV. Quick verification (David: “a couple of days from start to finish”). USB token included. |
| DigiCert OV (via GoGetSSL) | ~$730 incl. $120 shipping | ~$243 | Yes — SafeNet 5110+ shipped | Vincent Parrett’s 2023 purchase. Once you order through GoGetSSL the request process lands on the DigiCert site. |
| DigiCert KeyLocker (cloud HSM, add-on to a DigiCert cert) | cert + $90/yr | cert + $90 | No — DigiCert-hosted | Cheapest cloud HSM rental, but DigiCert certificates are the most expensive on the market. The HSM is cheap; the cert is not. |
If you find something cheaper, please tell me — I will move it to the top of the list.
Update, September 2026: I bought it. Here is what actually happened.
Everything above was research. In September 2026 I went through with it and bought the Certum cloud OV for my own company. The certificate works, my installers are signed, and I hit a few walls that nobody warns you about before you pay. So this section is the real thing, with dates.
What I paid. I ordered on sslmentor.eu, the euro site, not the dollar one: €297 for 3 years, reverse charge VAT, invoice in euro, no card conversion fee. The same product on the dollar site was $348. If you are in the EU, use the euro site.
How long it took.
- 1 September — order placed.
- 10 September — paid by card; the order reached Certum the same evening.
- 11 September, morning — company register extract accepted.
- 11 September, 14:31 — identity check done with IDnow, on the phone, about five minutes.
- 15 September, 07:07 — certificate issued. Two business days after the identity check.
- 15 September, 10:12 — first EXE signed and verified. About three hours from the issue mail to the first signature, and one of those hours went on a mistake I describe below.
What I got. An RSA 4096 key — Certum chose the size, I was never asked. Valid 459 days, to 18 December 2027, with the subscription running to September 2029. The signing card is pinless: no PIN window appeared at the first signature. SimplySign Desktop and the phone app cost nothing extra.
The bad news nobody tells you before you pay
None of this is hidden — it is all on Certum’s and the reseller’s pages. It is just not on the page where you click Buy.
You cannot sign without a person and a phone. Ever. This is the big one. SimplySign opens a signing session that lasts two hours, and you open it by typing a six-digit code from the SimplySign app on your phone. From the reseller’s own FAQ: “Is it possible to have the certificate connected non-stop? No, it is not possible. SimplySign Desktop has an active secure connection established for 2 hours. A new token must then be generated in SimplySign App.” So: no unattended night builds, and no simple CI/CD signing. If your release pipeline runs on a build server with nobody watching, this product does not fit and you should look at Azure Artifact Signing instead. The FAQ itself tells you to consider “whether the ‘restriction’ of the length of the 2-hour window is sufficient” before buying — good of them, but it is buried.
5000 signatures per month, and crossing the line can get the certificate blocked. From Certum’s shop page: “for Code Signing products in the cloud, there is a certificate usage limit of 5000 signatures per month. Exceeding this limit may result in contacting you to inform you of the exceedance and possible blocking of the product in the month in which the limit was used.” One signature is one file, so a release that signs thirty executables and an installer costs thirty-one. Nobody shows you a counter anywhere, so I keep my own in the signing script. Two things I still do not know: whether “month” means the calendar month, and whether a failed attempt counts.
A “3-year” certificate is not a 3-year certificate. You already read this above, but here is what it feels like in practice: you buy a subscription, and about every 460 days you must remember to press reissue in the panel. It is free and it is one click, but nothing reminds you, and the new certificate has a new thumbprint. If your build script pins the old thumbprint, signing quietly stops working. Write the reissue date in your calendar the day you buy.
There is no test certificate. From the reseller FAQ: “a CODE certificate for testing cannot be provided.” You find out whether the two-hour window and the monthly limit fit your workflow only after you have paid for three years.
Traps I fell into, so you do not have to
Scan the activation QR code from inside the SimplySign app, not with the phone camera. This cost me an hour. The camera happily recognized the code and handed it to a general authenticator app, which then produced six-digit codes that SimplySign Desktop refused with “Invalid user name or token”. The right way is: SimplySign app → Activate application → Other activation methods → Scan QR code. The mail does say “Scan the QR code using SimplySign”, and it is very easy to read past.
The activation link dies after 24 hours, and the code inside it is single-use. Activate the moment the mail arrives. I tested the limits afterwards: the link itself still loaded 26 hours later, but the six-character code in the same mail was already spent and was refused. An old mail cannot give you the QR code back — only a new activation can, and for that you must write to your reseller.
The download is a bundle. Certum offers you “proCertum SmartSign + SimplySign Desktop”, a 274 MB installer. You only need SimplySign Desktop. Untick proCertum SmartSign in the installer.
Your firewall will break this in a way that looks like a server problem. I run a per-program firewall (TinyWall). With
signtool.exeblocked, you get “The specified timestamp server either could not be reached or returned an invalid response” — while the browser reaches that same server fine. Worse, signtool then leaves the file unsigned: no timestamp and no signature, not a signature missing a timestamp. WhitelistSimplySignDesktop.exetoo, not just signtool. And note that a new Windows SDK is a newsigntool.exeat a new path, so you get to do it again.Never press “Remove Certificate” in SimplySign Desktop. The reseller’s guide is blunt about it: “The certificate will be removed without replacement and cannot be restored!”
Signing over an old signature: do not use
/as. Plainsigntool signreplaces the old signature, which is what you want when you re-sign a file that carried your previous certificate.signtool sign /asappends, and the old signature stays the primary one — so Windows keeps showing the old publisher. I tested this on a file signed by my previous company.An expired session makes signing hang, not fail. SimplySign pops up its login window and
signtoolsits there waiting for it. In an unattended script that is a hung build, not an error you can catch.“47 days” is not about code signing. You will see the notice that from March 2029 certificate validity drops to 47 days. That is about SSL (website) certificates. The code signing number is the 460 days mentioned above.
If unattended signing is what you need, the honest answer is that Certum’s cloud product cannot do it today, and I have found no published route around it: Certum’s own documentation and FAQ say nothing about CI/CD, and the public container project that wraps SimplySign states plainly that a human with the phone app must still authenticate before the container can sign.
EV vs OV
An OV (Organization Validation) is much simpler to obtain and requires less documentation. An EV (Extended Validation) requires nine extra steps: verifying your public business phone number, length of time in business, registration number and jurisdiction, plus a domain fraud check, contact blacklist check, and a telephone call to authenticate the requestor.
The trade-off is reputation. An EV certificate gives your application instant SmartScreen trust — the blue banner from day one. An OV does not. With an OV your application builds reputation over time, as more users download it without setting off antivirus alerts. Some advice says to submit your OV-signed program to Microsoft for antivirus review to speed this up.
Vincent Parrett’s view in the DelphiPraxis thread, which I agree with: “EV seems like a waste to me”. For a small ISV, an OV plus patience for the SmartScreen reputation to build is the better deal.
My purchase history
The first time, I bought an EV from SSL.com. Years later, I bought an OV from KSoftware. Both are resellers — under the hood you actually buy from Comodo (now Sectigo). Sectigo was very slow. The verification took two full months. The phone check failed multiple times. Everything was cumbersome. Tech support didn’t have a clue what was going on — probably just somebody in a call center reading from a script.
The first eToken arrived on a USB smart card with a reader, which was painful to use. Stay away from sellers that force you to buy a USB reader. They charge around $130 for it (under “shipping and handling”), and they probably make more profit on the dongle than on the certificate itself.
The second certificate (OV from KSoftware, around 2022) was delivered by email as a PFX file — no electronic device needed. That arrangement worked great for me for three years, until the certificate expired in April 2025. And then I hit the wall: as the DelphiPraxis thread spelled out, the email-PFX option no longer exists. For the renewal I had to pick a new vendor and a new workflow. That is what triggered this rewrite.
How to sign your EXE file
I use Microsoft’s signtool.exe. To get it, download the Windows SDK ISO (about 1 GB), but you don’t have to install it — open the ISO and extract Windows SDK Signing Tools-x86_en-us.msi only. That is a mere 400 KB.
With Certum SimplySign installed (or any cloud signer that exposes the key as a smart card), the signing command is:
"c:\Program Files (x86)\Windows Kits\10\bin\10.0.22000.0\x64\signtool.exe" sign /fd SHA256 /sha1 <cert-thumbprint> /tr http://timestamp.digicert.com /td SHA256 My.exeThe /sha1 parameter picks the right certificate from the Windows Certificate Store by its SHA-1 thumbprint (you can copy this from the SimplySign panel after the certificate is installed).
Always add /tr for a timestamp. The DelphiPraxis thread caught me out on this — I signed a file without a timestamp once, and the signature stops being trusted on new computers the moment the certificate expires. With a trusted timestamp, signed binaries keep working forever, even after your cert expires. Use any of: http://timestamp.digicert.com, http://timestamp.sectigo.com, http://timestamp.globalsign.com/scripts/timstamp.dll.
For the old PFX-on-disk workflow (only relevant if you still hold a pre-November-2022 certificate that hasn’t expired yet):
"c:\Program Files (x86)\Windows Kits\10\bin\10.0.22000.0\x64\signtool.exe" sign /fd SHA256 /f MyCertificate.pfx /p MyPassword /tr http://timestamp.digicert.com /td SHA256 My.exeTo verify the signature:
signtool.exe verify /pa MyExeFile.exe
if %ERRORLEVEL% GEQ 1 echo This file is not signed.
You should see:
Successfully verified: MyExeFile.exeYou can also right-click the EXE in Windows Explorer and check the Digital Signatures tab — both your signature and the timestamp should be listed. Or upload to VirusTotal: it should report “The file has authenticode/codesign signature information.”
What happens after signing your EXE
Nothing dramatic. On Windows 10 and 11 I kept seeing the same “untrusted” SmartScreen dialog with only the Don’t run button for a while — no Continue. With an OV, you do not get instant trust; you have to earn it. My program had about 400 downloads per day at the time. After a while, I downloaded my own program and noticed the warning was gone. I never measured exactly when the flip happened — somewhere between a few weeks and a couple of months of consistent downloads with no antivirus complaints, the file went from red to blue.
Two notes from hard-won experience:
- Once a specific EXE earns blue-banner status, that reputation sticks to the file — even if the certificate that signed it later expires. New users downloading the same binary still see blue. This only holds while the EXE bits are unchanged: rebuild and you lose the reputation and start over.
- An EV skips this entire reputation-building phase. If your release cadence is so fast that no single EXE ever has time to build reputation before you replace it, the math may favor an EV after all. For most small ISVs releasing every few months, OV + patience is fine.
Sources and further reading
- DelphiPraxis — “New Code Signing Certificate Recommendations” — the thread that pushed me to rewrite this article. Vincent Parrett, David Heffernan, Angus Robertson, DelphiUdIT and others share real purchase prices and token-vs-cloud experiences.
- Vincent Parrett — Code signing with USB tokens (FinalBuilder blog) — the canonical reference for automating
signtool.exewith SafeNet tokens. - DigiCert — 459-day validity alert.
- Certum — shortening validity notice.
- Certum — signing with signtool and jarsigner (official how-to).
- CA/Browser Forum — code signing baseline requirements.
Read more about packaging and shipping Delphi applications in my books.